Pleniko Blog
AI with Human Approval: How Businesses Can Automate Without Losing Control
- Artificial Intelligence
- Human Oversight
- Business Automation
- Responsible AI
- Decision Support
- Internal Systems
- AI Governance
- Digital Transformation
 AuthorPlamen Nikolov
Artificial intelligence is increasingly being added to internal systems, administration panels, CRM and ERP platforms. It can process documents, summarise communication, identify anomalies and suggest next actions within seconds.
This creates an opportunity to reduce repetitive work substantially. It also raises an important question: which actions can be fully automated and which should remain under human control?
For most businesses, the right answer is neither rejecting AI nor adopting uncontrolled automation. A more practical approach allows AI to prepare, analyse and recommend while a responsible employee reviews and approves actions with real consequences.
Automated does not mean uncontrolled
Traditional automation executes predefined rules. If an invoice is overdue, the system sends a reminder. If an order is paid, its status changes. The result is predictable because the conditions and actions have been defined in advance.
AI works differently. It can interpret unstructured text, images and large datasets, but its output is often a probabilistic recommendation rather than a guaranteed fact. The same model may produce different results depending on context, supplied data and task formulation.
AI output should therefore not automatically become an irreversible business action. The system must distinguish clearly between:
This distinction allows employees to benefit from AI speed without accepting its conclusions uncritically.
AI is most useful as a preparation assistant
AI can handle much of the preliminary work inside a business system. Suitable examples include:
For these tasks, AI saves time while the result remains a proposal. The user sees the relevant sources, verifies important values, and decides whether to accept, edit, or reject the output.
When is human approval essential?
Not every AI operation carries the same risk. Automatically organising internal notes does not have the same consequences as rejecting a customer request or approving a payment.
Human approval should be required when an action:
The more serious the consequences, the clearer the control point must be. One employee may be sufficient for some decisions. Higher-risk actions may require a second approval, a specific role or an additional verification step.
A good system provides more than an Approve button
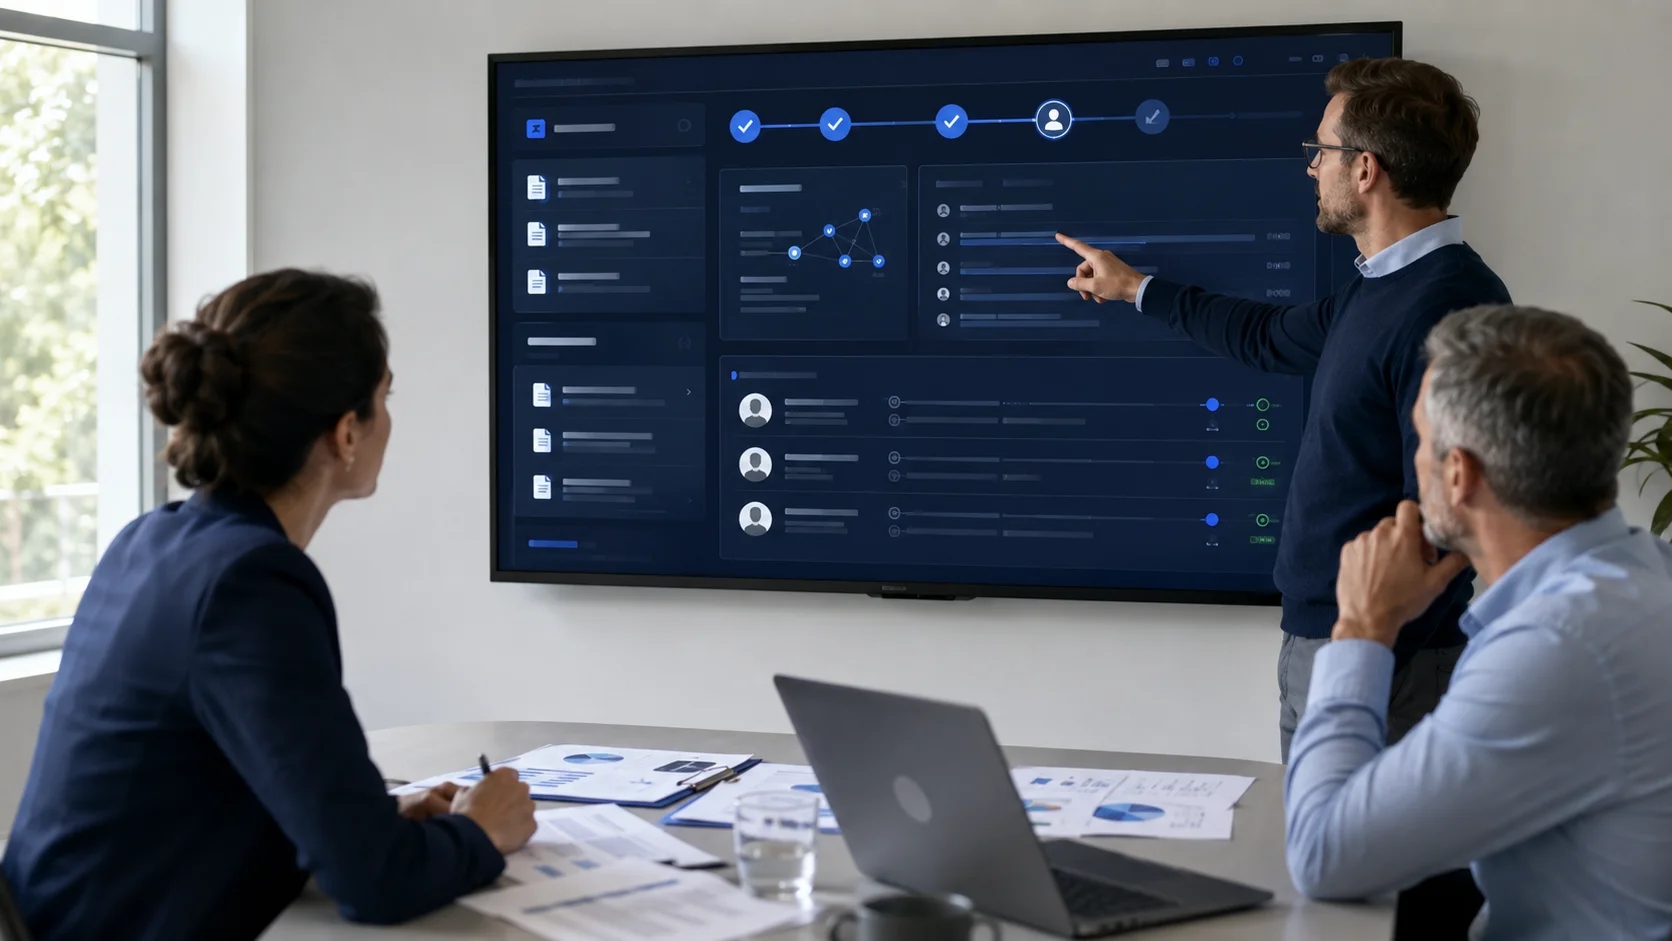
Human involvement has little value when the employee lacks enough information to perform a genuine review. The approval screen should provide context instead of merely transferring responsibility to the user.
An appropriate interface displays:
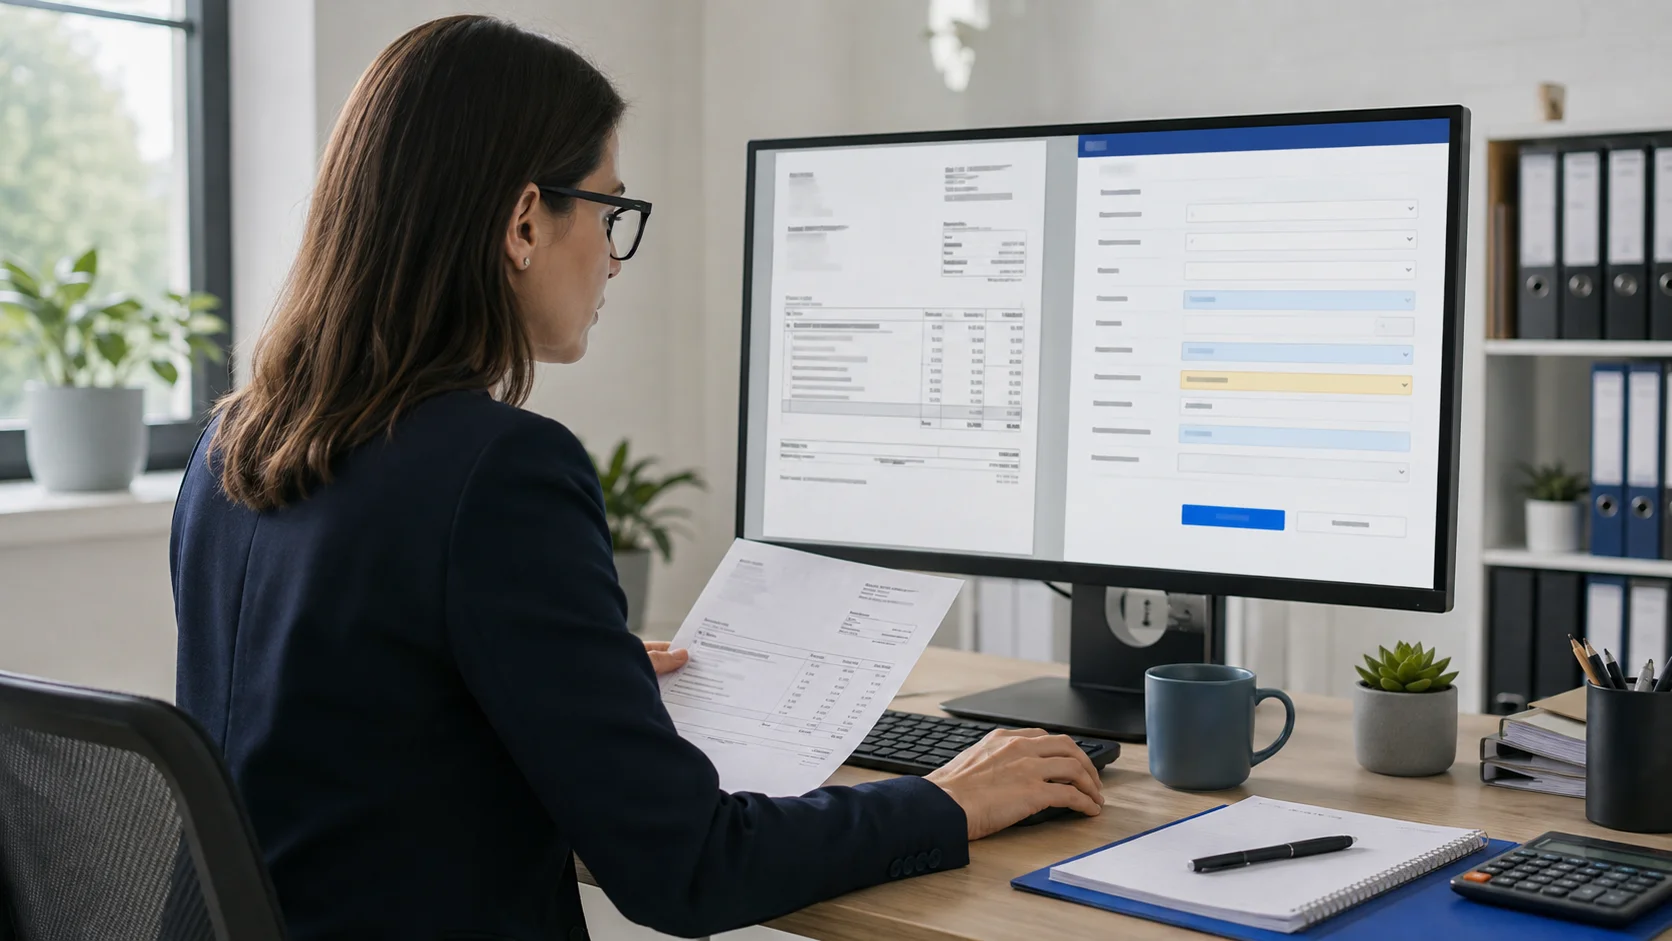
When processing an invoice, for example, the employee should see the original document and extracted fields at the same time. For an AI-generated customer response, the employee needs access to previous communication and the ability to edit the draft before sending it.
Three practical levels of automation
Rather than building every AI feature in the same way, organisations can separate them by risk.
Level 1: AI provides information
AI summarises, searches or explains without modifying data or triggering an action. The user treats the result as supporting information.
Level 2: AI prepares a recommendation
The system completes a draft, suggests a category, flags a risk or prepares a sequence of actions. Nothing is executed until a person reviews and confirms the recommendation.
Level 3: AI performs limited and reversible actions
When risk is sufficiently low, the system may execute a clearly bounded operation automatically. Rules, monitoring, an audit trail, and a rapid stop or recovery mechanism remain necessary.
This model allows automation to expand gradually. A feature may begin as a recommendation only. After measuring accuracy and real errors, some low-risk cases can be automated while exceptions continue to be directed to a person.
This creates an opportunity to reduce repetitive work substantially. It also raises an important question: which actions can be fully automated and which should remain under human control?
For most businesses, the right answer is neither rejecting AI nor adopting uncontrolled automation. A more practical approach allows AI to prepare, analyse and recommend while a responsible employee reviews and approves actions with real consequences.
Automated does not mean uncontrolled
Traditional automation executes predefined rules. If an invoice is overdue, the system sends a reminder. If an order is paid, its status changes. The result is predictable because the conditions and actions have been defined in advance.
AI works differently. It can interpret unstructured text, images and large datasets, but its output is often a probabilistic recommendation rather than a guaranteed fact. The same model may produce different results depending on context, supplied data and task formulation.
AI output should therefore not automatically become an irreversible business action. The system must distinguish clearly between:
- information extracted from a verifiable source;
- a value calculated through an explicit rule;
- a recommendation produced by AI;
- a result reviewed and confirmed by a person.
This distinction allows employees to benefit from AI speed without accepting its conclusions uncritically.
AI is most useful as a preparation assistant
AI can handle much of the preliminary work inside a business system. Suitable examples include:
- extracting data from invoices, contracts and applications;
- summarising long correspondence;
- preparing a draft response;
- categorising requests and documents;
- detecting potential duplicates;
- comparing contract versions;
- flagging unusual values or behaviour;
- suggesting the next workflow step;
- preparing key observations from a report;
- searching a large collection of internal documentation.
For these tasks, AI saves time while the result remains a proposal. The user sees the relevant sources, verifies important values, and decides whether to accept, edit, or reject the output.
When is human approval essential?
Not every AI operation carries the same risk. Automatically organising internal notes does not have the same consequences as rejecting a customer request or approving a payment.
Human approval should be required when an action:
- creates a financial obligation or executes a payment;
- changes a contract, price or significant customer commitment;
- affects hiring, employee evaluation or termination;
- grants or removes access to sensitive information;
- sends official communication on behalf of the company;
- changes medical, legal or other specialised information;
- can affect a person's rights, services or opportunities;
- deletes information or performs a difficult-to-reverse operation;
- relies on incomplete, conflicting or low-confidence information.
The more serious the consequences, the clearer the control point must be. One employee may be sufficient for some decisions. Higher-risk actions may require a second approval, a specific role or an additional verification step.
A good system provides more than an Approve button
Human involvement has little value when the employee lacks enough information to perform a genuine review. The approval screen should provide context instead of merely transferring responsibility to the user.
An appropriate interface displays:
- the original data or document;
- the AI recommendation;
- which values were extracted and which were generated;
- the sources used for the recommendation;
- detected inconsistencies and missing information;
- a confidence indication when it is meaningful and properly calibrated;
- the consequences of confirmation;
- options to accept, edit, reject or escalate.
When processing an invoice, for example, the employee should see the original document and extracted fields at the same time. For an AI-generated customer response, the employee needs access to previous communication and the ability to edit the draft before sending it.
Three practical levels of automation
Rather than building every AI feature in the same way, organisations can separate them by risk.
Level 1: AI provides information
AI summarises, searches or explains without modifying data or triggering an action. The user treats the result as supporting information.
Level 2: AI prepares a recommendation
The system completes a draft, suggests a category, flags a risk or prepares a sequence of actions. Nothing is executed until a person reviews and confirms the recommendation.
Level 3: AI performs limited and reversible actions
When risk is sufficiently low, the system may execute a clearly bounded operation automatically. Rules, monitoring, an audit trail, and a rapid stop or recovery mechanism remain necessary.
This model allows automation to expand gradually. A feature may begin as a recommendation only. After measuring accuracy and real errors, some low-risk cases can be automated while exceptions continue to be directed to a person.
Human approval must not become a formality
When a system presents too many recommendations, users may begin confirming them mechanically. This is automation bias: the person assumes that a recommendation is correct because it comes from an automated system.
The interface should direct attention to material information. Low-confidence values are highlighted, important differences are clearly presented, and unusual cases are separated from routine work.
Not every employee should approve every recommendation. The task must reach a person with appropriate knowledge, permissions, and responsibility. The system should also measure review time so that it does not create a new administrative bottleneck instead of a genuine improvement.
Traceability for every AI-assisted decision
When AI participates in a business process, the organisation must be able to establish what happened. An appropriate audit record may include:
- when the recommendation was created;
- which function or model was used;
- which configuration version was active;
- which sources were supplied;
- what output was returned;
- which employee reviewed it;
- whether it was accepted, edited or rejected;
- which action followed approval.
This history supports error investigation, process improvement, customer cases and internal control. It also allows the organisation to measure whether the AI feature provides genuine value.
The audit trail should not record passwords, tokens or unnecessary personal information. Access is restricted by role, while retention is defined according to purpose and organisational requirements.
AI should have limited permissions
One of the most important architectural measures is ensuring that an AI component receives no more access than it needs. If its task is to summarise customer communication, it has no reason to approve payments or modify user roles.
An appropriate design uses:
- separate tools for specific actions;
- minimum permissions for every AI process;
- limits on which records can be read or modified;
- validation of parameters before execution;
- human confirmation for sensitive operations;
- limits on action volume and frequency;
- termination when an unexpected result occurs;
- protection from instructions hidden in external documents or content.
AI should not have direct and unrestricted access to the primary database. Actions pass through a controlled application layer that enforces permissions and business rules in the same way it would for a regular user.
Protecting company and personal information
Before information is sent to an external AI service, the organisation must determine whether it contains personal data, trade secrets, medical information, contractual terms or other sensitive elements.
Practical measures include minimising the supplied data, removing unnecessary identifiers, encrypted communication, contractual restrictions, control over retention periods and a clear definition of how the information may be used.
A local model or specially isolated environment may be appropriate for some processes. In other cases, a dependable external service is more practical. The choice depends on data sensitivity, required accuracy, infrastructure and cost.
Quality must be measured with real cases
A demonstration using a few selected examples is not sufficient. Before an AI feature becomes part of daily work, it must be tested with realistic and diverse cases.
Relevant measurements include:
- the percentage of correctly extracted or categorised information;
- the frequency of missed risks and false alerts;
- how often employees edit recommendations;
- how much time is saved after review is included;
- which document types or situations create problems;
- how behaviour changes after a model update;
- whether different user groups receive unjustifiably different results.
A safe fallback process is also necessary. If the AI service is unavailable, returns an invalid response or has low confidence, the task should return to the standard manual workflow without losing data.
Transparency is increasingly important in 2026
Organisations need to indicate clearly when users are interacting with AI and when content has been generated or substantially altered by such a system. Transparency should be treated not only as a regulatory requirement but also as part of trust in the product.
Employees should know when they are viewing an AI recommendation, and customers should not be misled into believing that automatically generated communication was personally written by a specific individual. Higher-risk applications require additional assessment, documentation and human-oversight mechanisms.
Specific obligations depend on the company's role, the system being used and its intended purpose. Implementation should therefore be evaluated against current rules and the real context rather than a general statement that the organisation “uses AI”.
How is this process implemented technically?
Within a Symfony and React business system, AI can be integrated as a separate controlled component. The backend prepares the minimum necessary context, sends the request and validates the response. The recommendation is stored separately from confirmed business data.
The React interface displays the source and recommendation side by side, highlights uncertain elements, and provides actions to accept, edit, reject, or escalate. Only after confirmation does Symfony execute the permitted business operation through the standard access-control and validation rules.
Heavier analyses can run through queues and workers. The user does not need to keep a page open and instead receives a notification when a recommendation is ready for review. Every stage is recorded in the audit trail.
This approach does not bind the entire system to one AI provider. The integration layer can support different models according to the task, price, data sensitivity, and required quality.
How do we approach AI at Pleniko?
At Pleniko, we do not add AI simply because the technology is popular. We first identify the specific process, the time currently being lost, the quality of available data, and the consequences of a potential error.
We then select the appropriate level of automation. For low-risk tasks, AI can support search and summarisation. For documents, communication and classification, it prepares a recommendation for review. For actions with financial, contractual or other significant consequences, we retain a clear human approval point.
The objective is to use the strengths of AI — speed, high-volume information processing and pattern recognition — without removing accountability, professional judgement and the ability to intervene.
The right automation keeps people in the process
AI can save substantial time and help employees work with more information. Its benefit is greatest when the technology is integrated into a clear and measurable process.
A good business system does not hide the involvement of AI or automatically execute every recommendation. It presents sources, highlights uncertainty, restricts permissions, records actions and directs important decisions to an appropriate person.
Automation then does not replace control. It creates more time for judgement, communication and the decisions for which human responsibility remains essential.